Top Azure DevOps Tools Every DevOps Engineer Should Know in 2026
Last updated on Oct 7, 2026
To operate in the enterprise software industry in the year 2026, one must develop an ecosystem of continuous delivery based on resiliency, sovereign cloud security, platform engineering, and AI. Although Azure DevOps has been a recognized standard for end-to-end development management, the requirements of cloud architecture and compliance have changed the way teams work with this platform. Engineers today are no longer involved in the mere writing of pipeline configurations, but are actively involved in developing self-service internal developer platforms, implementing policies in line with code, managing container runtimes in the cloud, and integrating security systems into every phase of the commit process.
Those who want to master Azure DevOps should learn its native features and the wider context of the different specialized tools. From automated provisioning to GitOps controllers, and from zero trust secrets management to proactive observability, the tools described here constitute the toolchain of the future and should be known by everyone working with Azure DevOps in its 2026 vision.
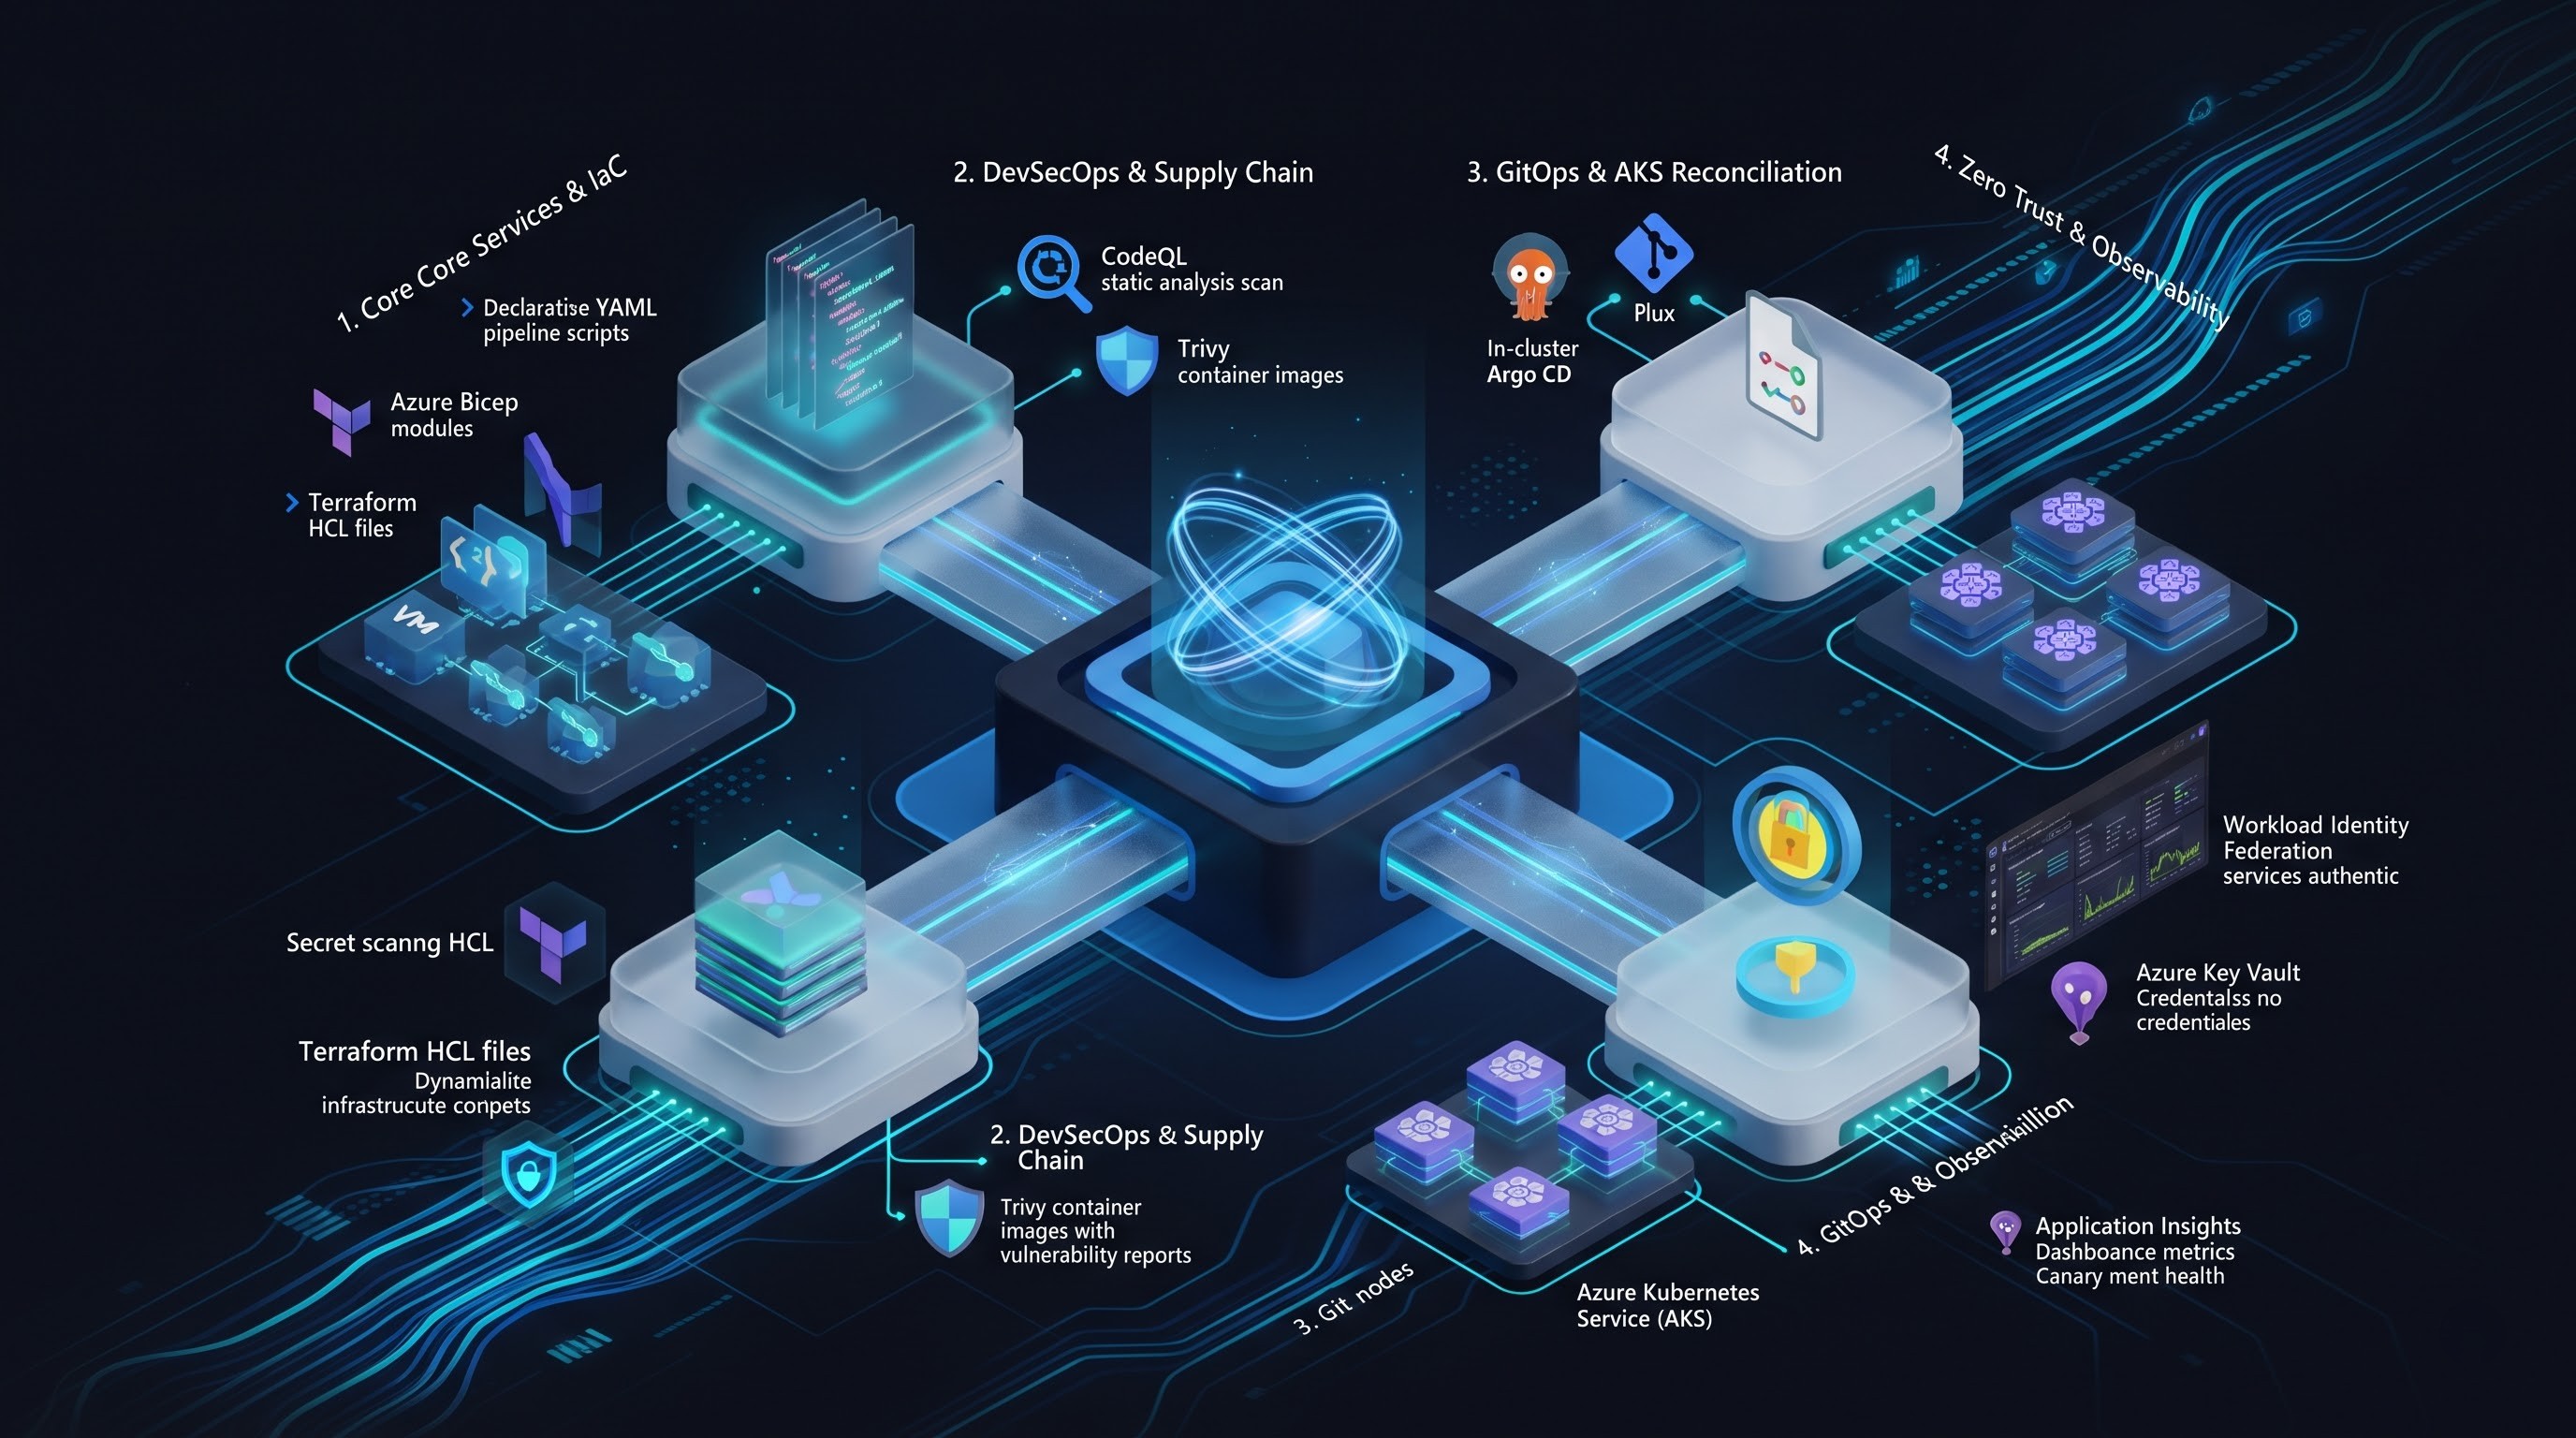
To completely master this multi-tool ecosystem, one has to possess in-depth practical knowledge about both cloud architecture and continuous integration flow. To help engineers grasp this bridge between theory and production-ready deployment of the enterprise through hands-on experience, OnlineITGuru has a well-structured and lab-oriented azure devops training program.
Fundamental Azure DevOps Core Services
Before exploring ecosystem plug-ins, every DevOps specialist should first be proficient in the five core American DevOps module tools. The core instruments described have gone through advancements with advanced cloud-scale intelligence and Microsoft ecosystem telemetry.
Azure Pipelines
Azure Pipelines is still working as the coordination basis of the platform providing the training of how to implement continuous integration and deployment in hybrid settings, private clouds or multi-cloud targets. As of 2026, contemporary pipelines are based on the exclusively declarative YAML definition, breaking old graphical descriptions in favor of the version-controlled pipeline as a piece of code. The modern pipeline engineer works with the re-usable templates depot, versions of libraries connected to national stores, and containerized tasks which isolate processes. This function is innate for the platform providing flexible builds and environments with approval locks and service connection tools based on the federated OpenID Connect tokens which do not allow using long-term granting letters.
Given that the architecture of the YAML pipeline is the basic underlying principle of modern continuous delivery, individuals who want to learn the art of template reuse, pipelines as code, and federated workload identities can benefit from the complete azure devops training online at OnlineITGuru.
Azure Boards
Enterprise organizations utilize Azure Boards for planning and tracking issues. Unlike being regarded as just a ticketing application, Azure Boards in 2026 operates as an effective governance and value stream management solution. Various work items like bugs, user stories, and epics are paired with code branches, pull requests, automated tests, and deployment methods. Engineers accept process designs and state transitions depending on approved pull requests and various analytic methods to automate and simplify monitoring delivery time frames and recovery time.
Azure Repos
The Azure Repos platform provides businesses with professional Git repositories that have advanced branch management features, allowing collaboration on code discussion. The system employs branch policies that require participation from reviewers of requests and validation of builds. It can be integrated with different Microsoft programs using Microsoft Entra for authorization and access levels management.
Azure Artifacts
In modern times, apps rarely function solely; they require packages, libraries, and frameworks. Azure Artifacts brings universal package management for well-known package types, including container base layers, universal packages, and language-specific distributions. Azure Artifacts serves as upstream proxy in business situations and helps to keep public dependencies within the perimeter of the business organization. It helps in ensuring compliance with licenses, protection of pipelines from upstream service failures, and prevention of malicious software supply chain attack.
Azure Test Plans
Quality engineering is an important component of continuous delivery, and Azure Test Plans connects automated testing and testing practices. It enables teams to plan, manage, and implement manual testing processes and link the results to the pipelines. Azure Test Plans also enhances the bug reporting process for web and desktop apps with extensive capabilities.
Infrastructure as code and automated provisioning
The modern approach of platform teams is to consider infrastructure as a direct analogue to application source code. Provisioning of cloud environments via click-and-point methods is a total thing of the past now. The following tools are the main players in the Domain of infrastructure as code used with Azure DevOps.
Azure Bicep
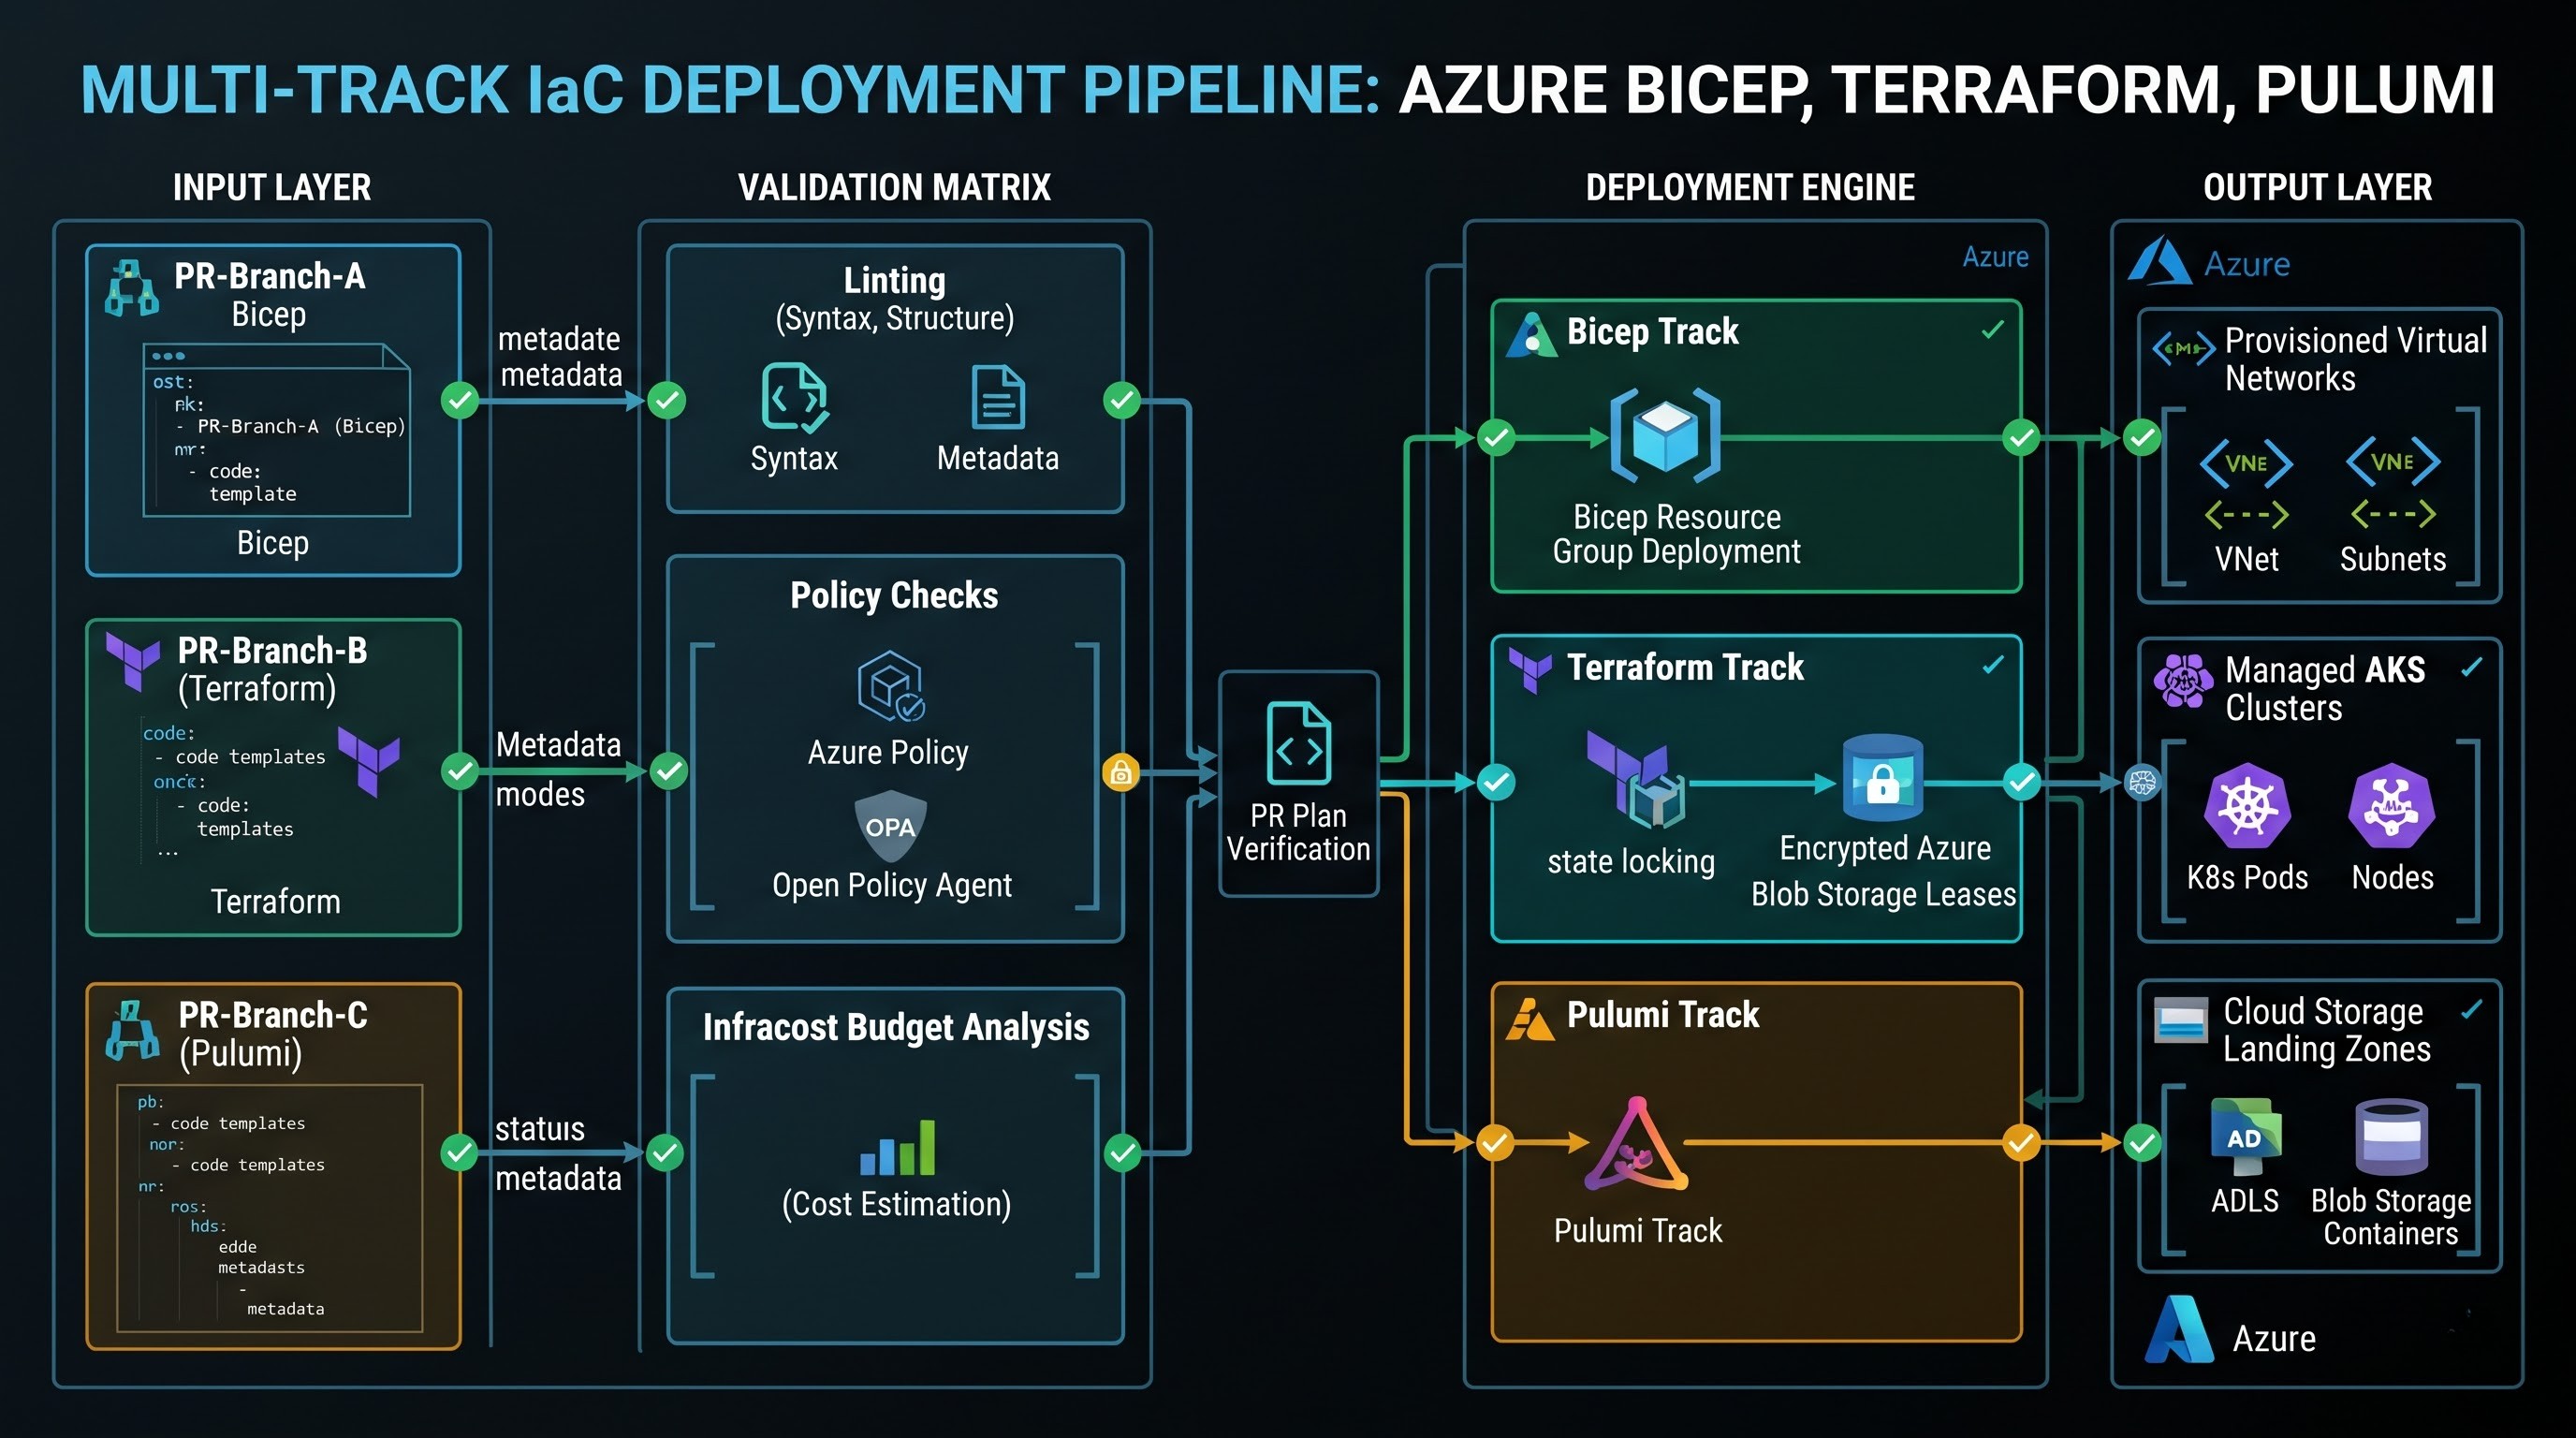
Azure Bicep is a programming language of Microsoft specifically created to provision Azure resources in a declarative manner. Azure Bicep language provides ease of use and abstracts away the complicatedness of using just regular Azure resource manager templates (ARM). In the present-day pipelines Bicep files are normally validated by means of the linting task, executed at resource group levels and going through pre-deployment comparison practices that give the chance to see in advance what will be changed in the infrastructure state.
HashiCorp Terraform
In the case of organizations that have multi-cloud or hybrid provisioning needs which mean connection of the cloud fabrics to on-premise machinery, HashiCorp Terraform is a tool that is instead just a standard. The Azure Resource Manager (ARM) provider allows enterprises to codify the enterprise landing zones, software-defined network, and clustered computing pools. In Azure DevOps, developers create automated pipelines executing validation and forming execution plans for the Terraform scripts, and the generated execution plans are posted back to the pull request threads and modified only after getting the necessary approvals. The state of Terraform tools is stored in an encrypted Azure Blob storage account through the implementation of active state locking offered by storage leases.
Pulumi
Pulumi is one of the popular choices of cloud architects who prefer working with ordinary programming languages rather than markup languages. The opportunity of building Azure cloud with computer software allows programmers to apply engineering concepts such as inheritance, looping, library modules, and unit testing during the infrastructure creation. Integration of Pulumi in Azure DevOps enables the team to test their cloud infrastructure as well since the testing process is included in the pipeline.
DevSecOps and the Security of Software Supply Chains
The security of a software supply chain cannot be underestimated. In 2026, security will not be an audit procedure carried out after the system deployment. Instead, security will become a part of the regular procedures of software development and deployment.
GitHub Advanced Security for Azure DevOps
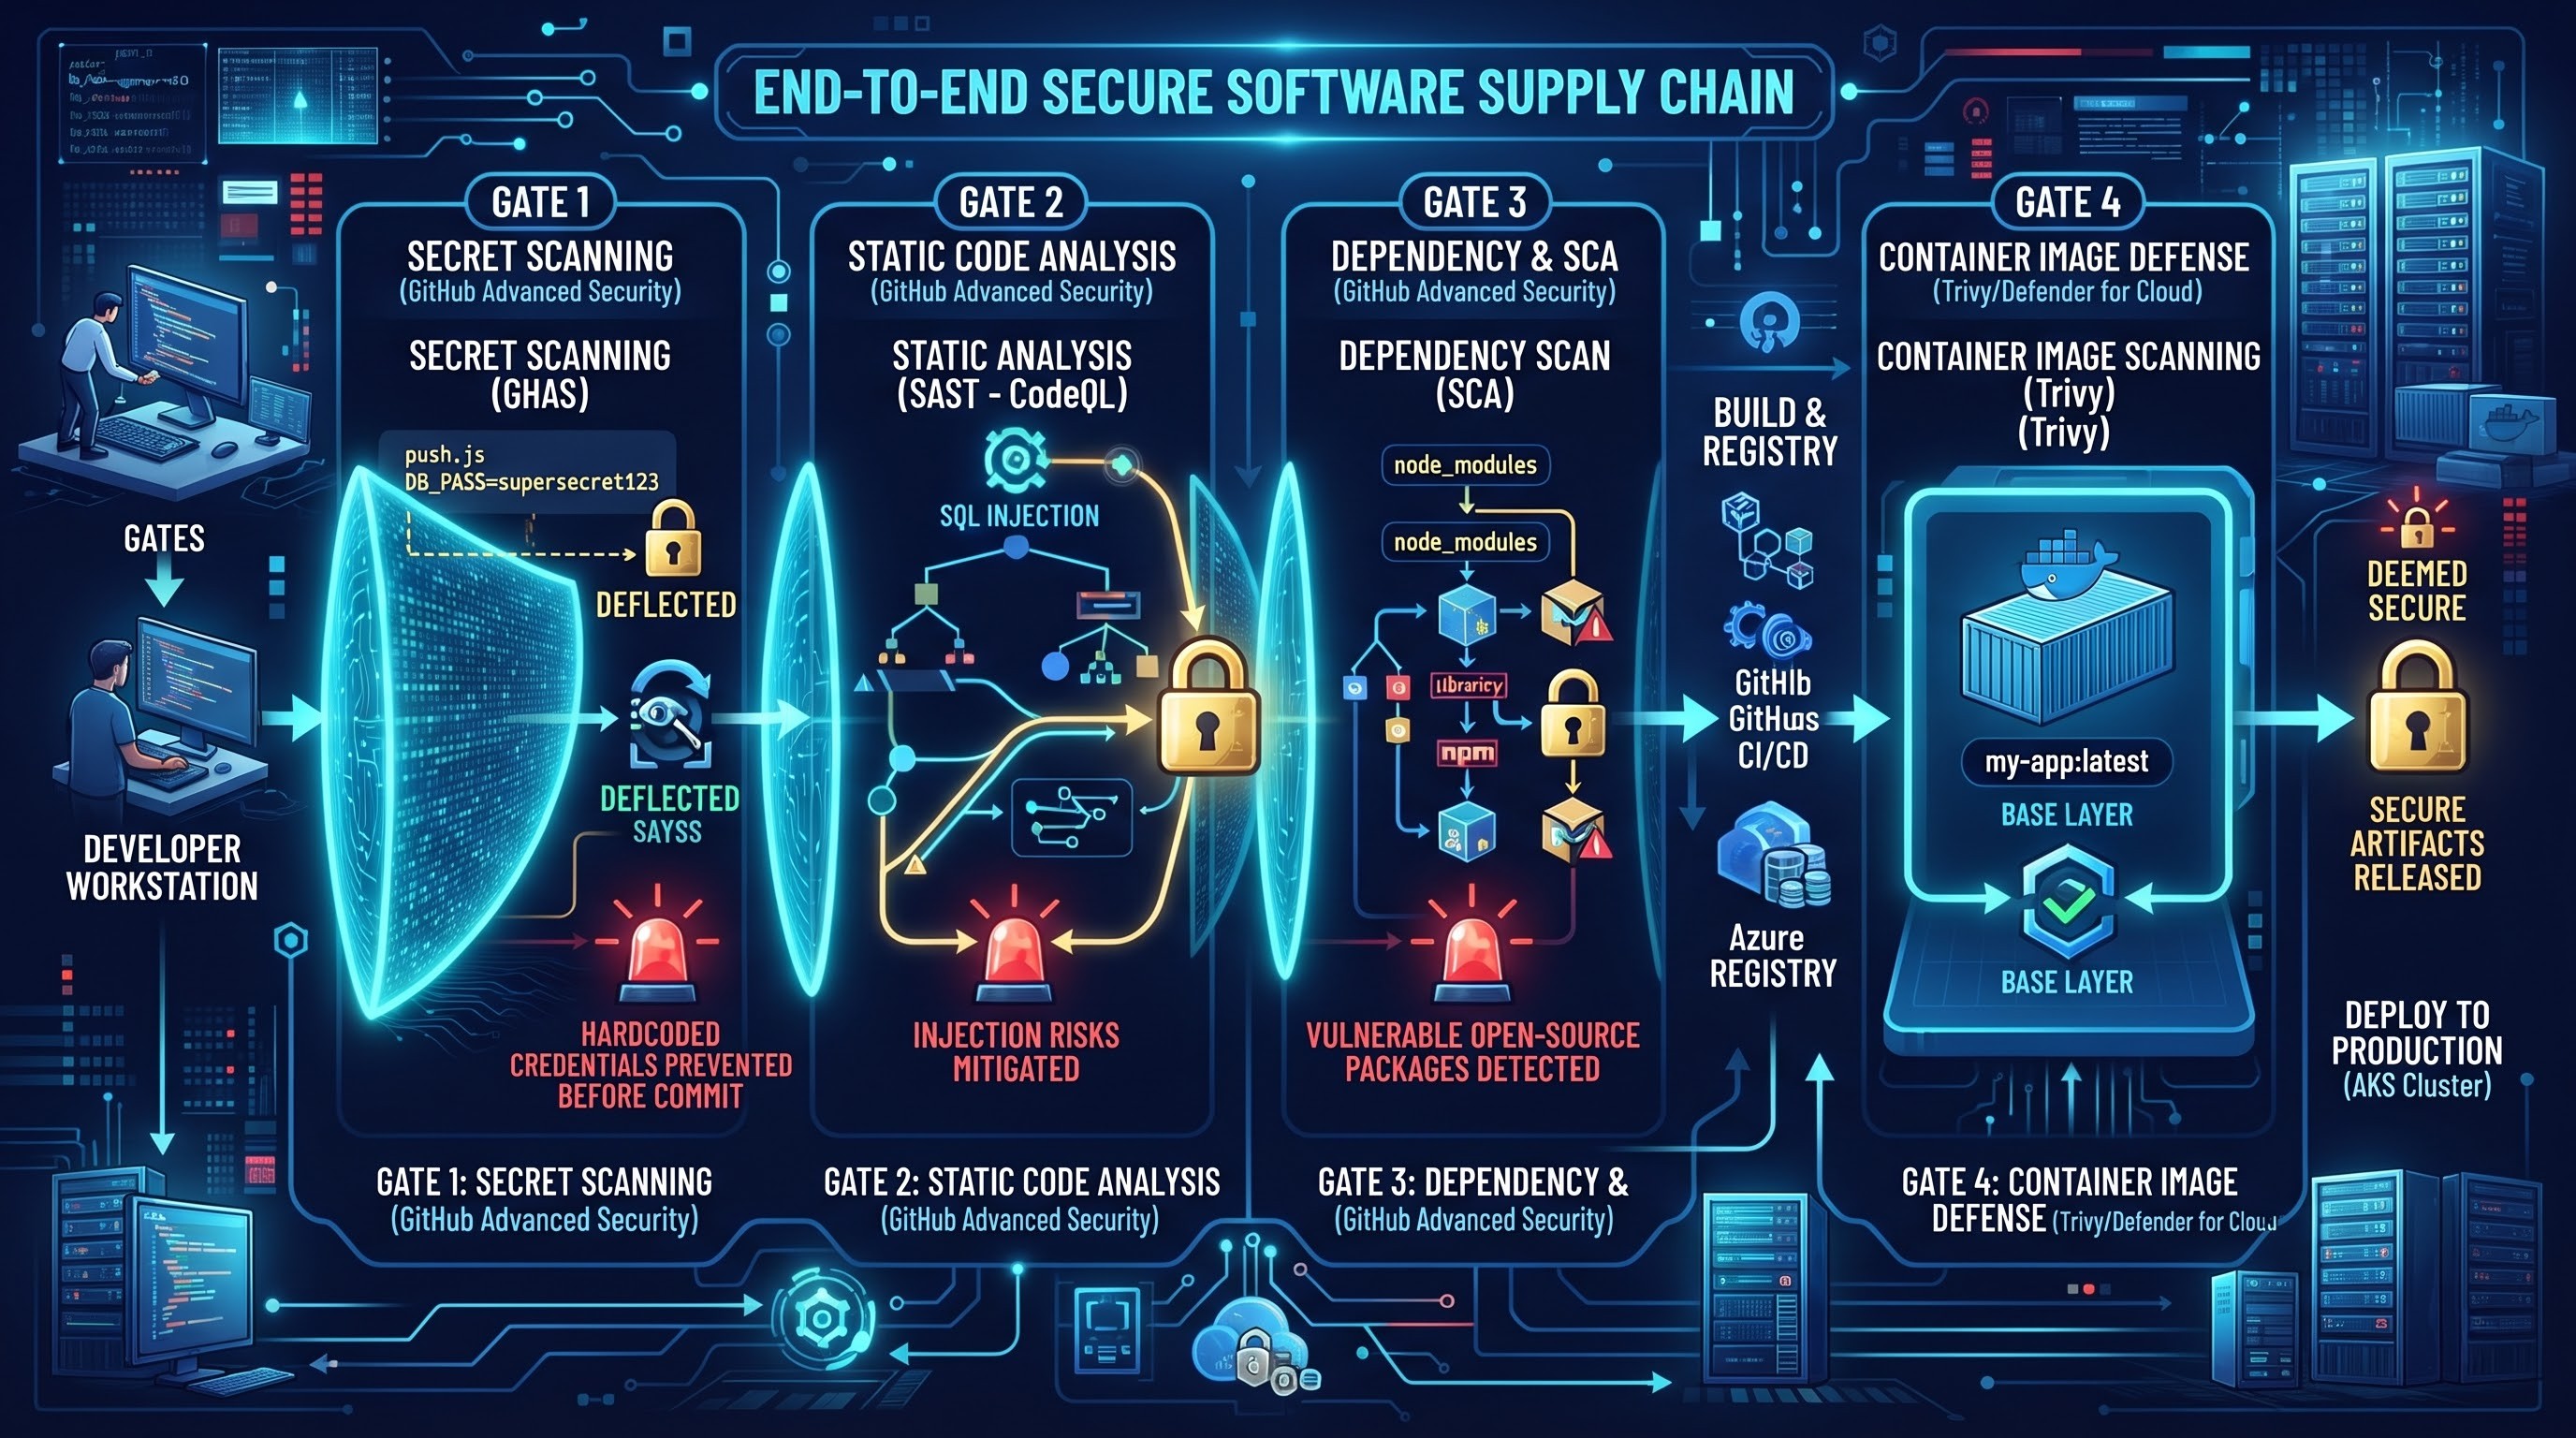
GitHub Advanced Security for Azure DevOps incorporates security scanning capabilities into Azure DevOps. The following are the three major security capabilities provided by this tool:
Secret Scanning: It helps detect the presence of any forgotten passwords, certificate, and connection strings in order to avoid pushing sensitive data by mistake.
Dependency Scanning: It compares third party open source libraries against defensive vulnerability databases where any potential security threats will generate a report.
CodeQL Static Analysis: It analyzes the software code thoroughly to analyze the execution path of the software.
Microsoft Defender for Cloud and Microsoft Security DevOps
The Microsoft Security DevOps extension is a component of the Microsoft Security DevOps platform that enables security automation during CI/CD processes. By operating with Microsoft Defender for Cloud, the synergy creates a closed-loop end-to-end security process. It makes it possible to analyze containers’ images and security backdoors, as well as to compare security parameters of the cloud-based system under scrutiny with the security requirements and benchmarks. The differences in pipeline configuration and security posture baselines are reported in the build reports, which allows engineers to eliminate misconfigurations before the launch of cloud services.
SonarQube and SonarCloud
SonarQube and its managed service, SonarCloud, remain the gold standard for code quality, code structure, and code vulnerability continuous analysis. Integrated into Azure Pipelines, SonarQube acts as a mandatory gateway that ensures that every pull request is being reviewed for code quality violations such as duplicated algorithms, outdated technologies, and limited test coverage. The process allows engineers to eliminate bugs before launching cloud applications and prevents developers from accumulating technical debt.
Trivy
Trivy, which comes from Aqua Security, is known as a lightweight and versatile solution for vulnerability detection and misconfiguration issues in today's containerized environments. It gets executed in Azure DevOps pipelines as soon as containers are built, but before being published to the artifact repository. The scanner checks the presence of issues in the packages installed in the container operating system, dependencies, and configuration layers. Its speed and huge database makes it a perfect solution for vulnerability checks within the continuous deployment pipeline.
Container Orchestration and GitOps Delivery
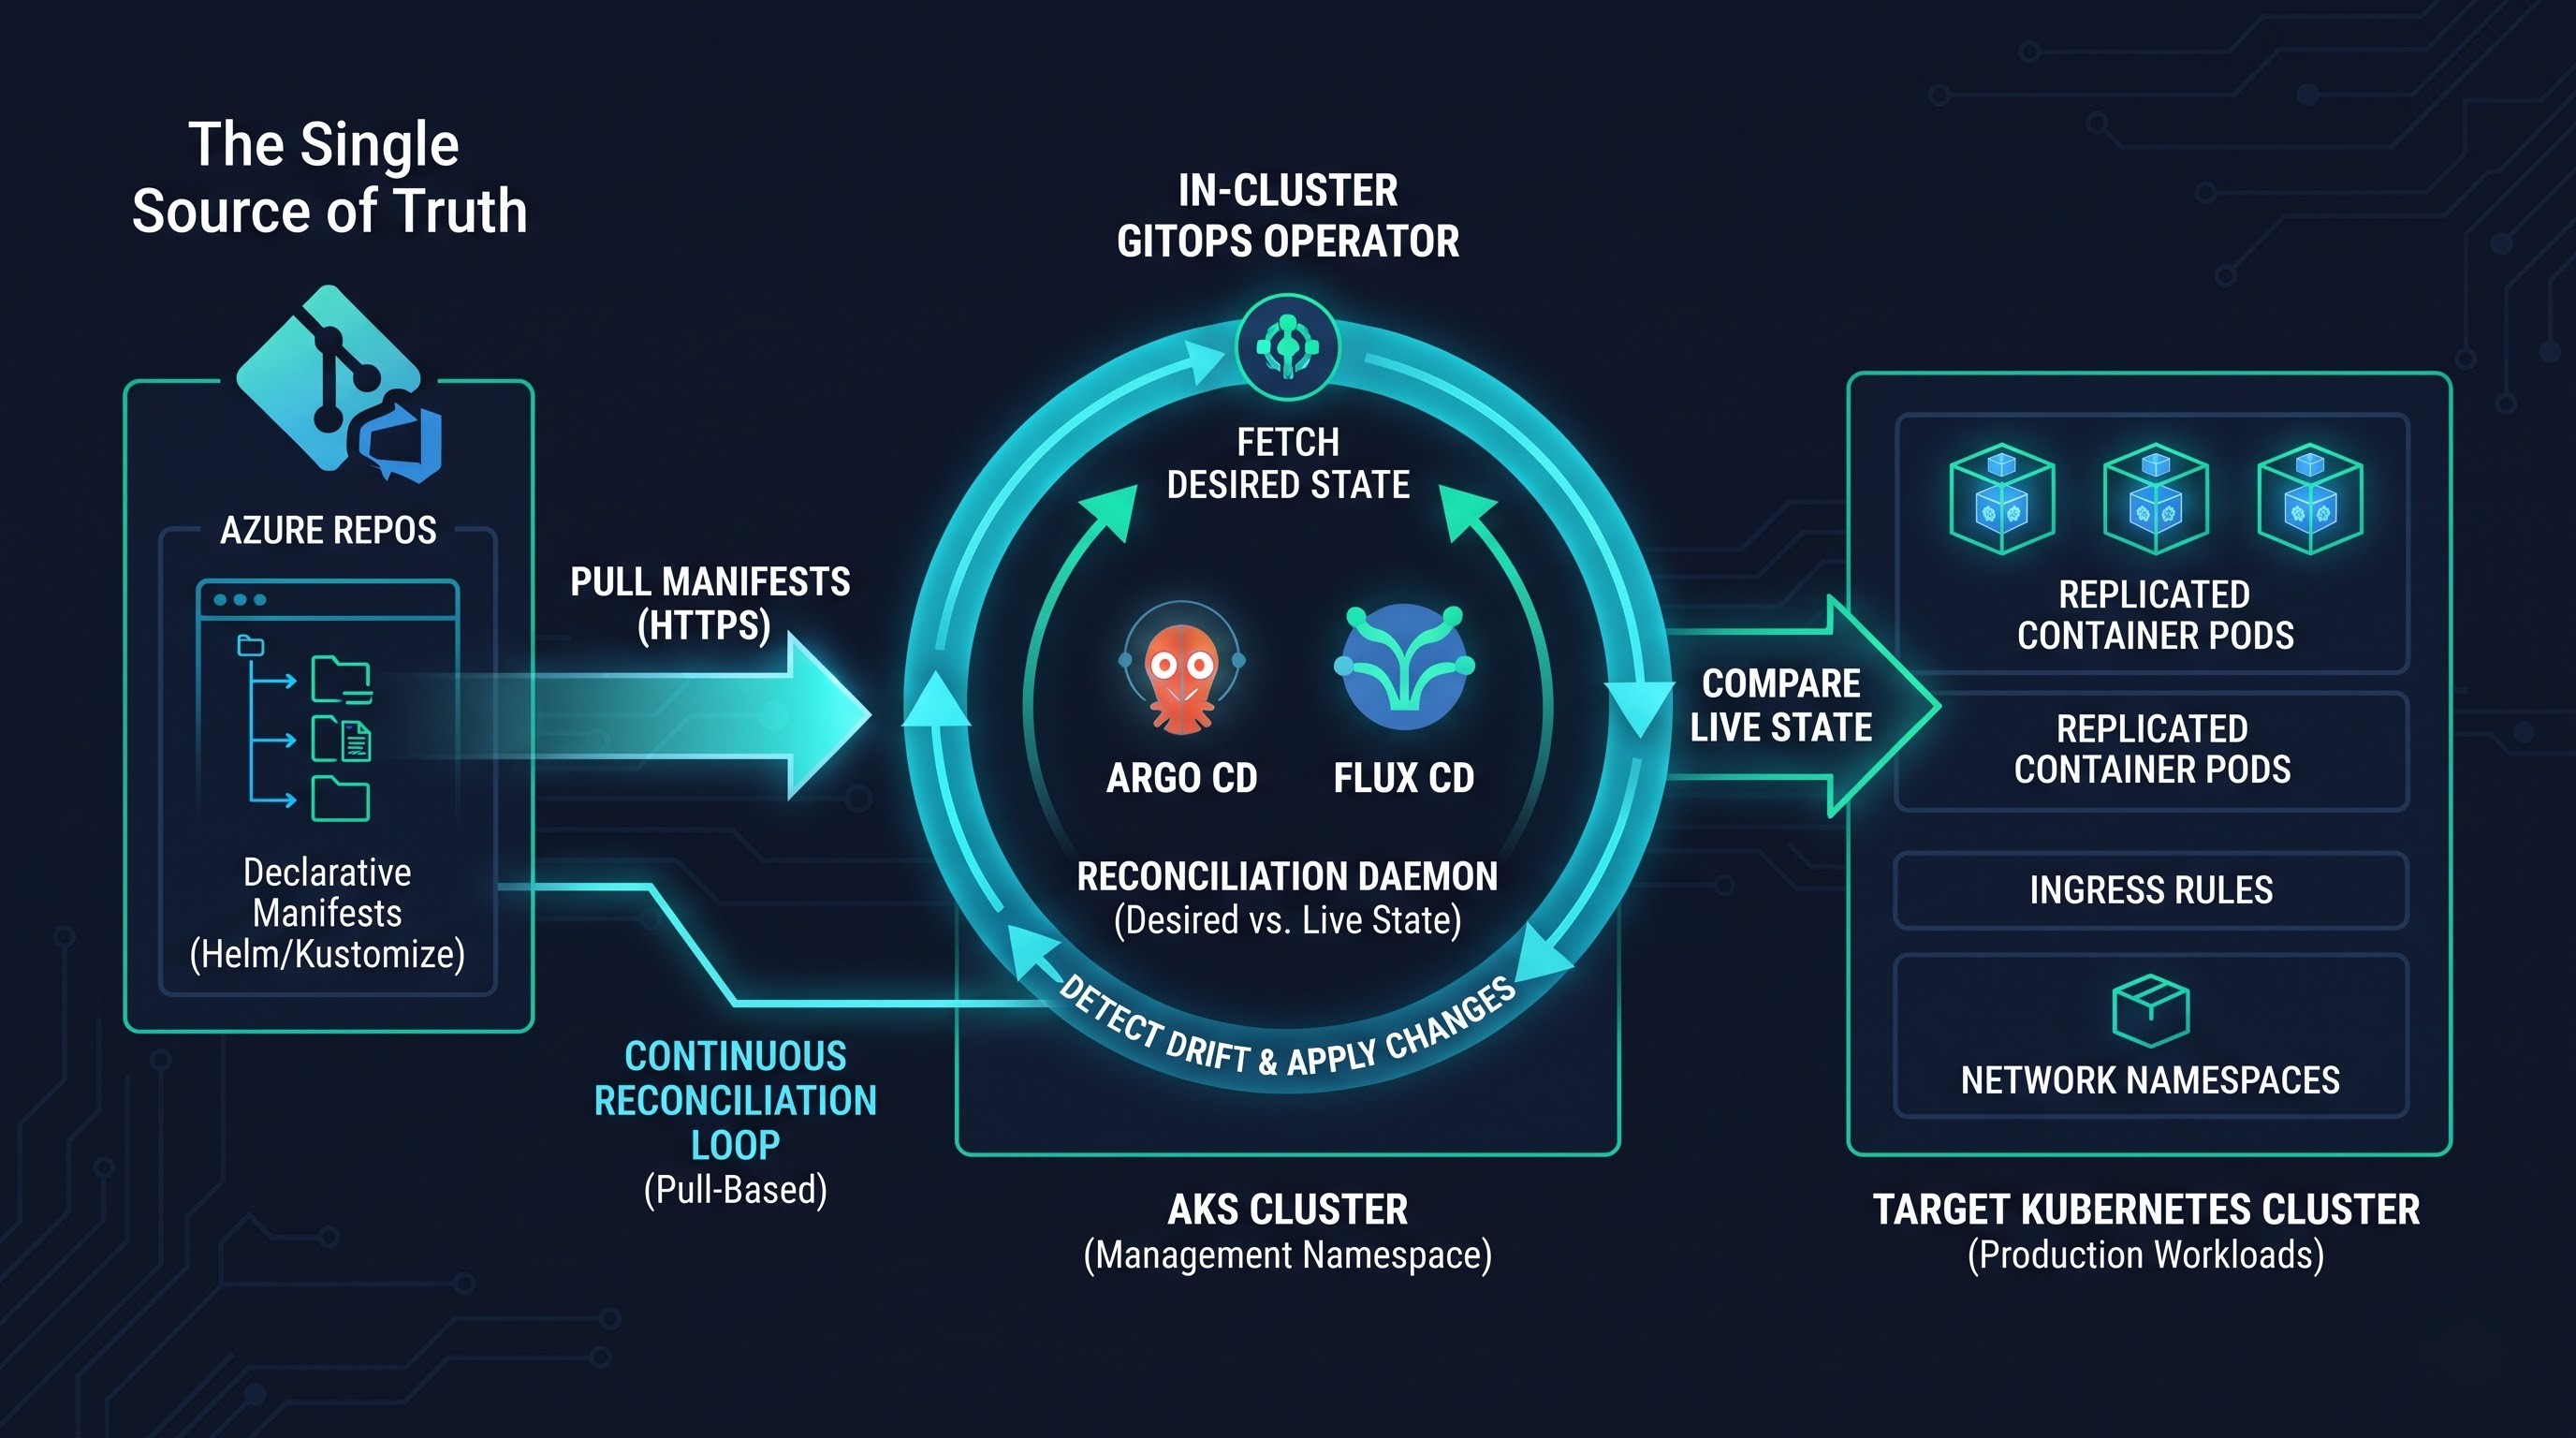
Due to the growing popularity of microservices and containerized applications, the deployment pipelines have switched from sending commands to using the concept of continuous reconciliation in working with important tasks.
Delivery Tools for Azure Kubernetes Service (AKS)
Azure Kubernetes Service provides the backbone of enterprise application deployment. Developers have access to unique Azure DevOps marketplace activities and command-line tools when working with AKS. Some examples include Helm for building complex Kubernetes application models packaged into released versions along with Kustomize for managing configurations based on specific environments without changing the original files. Azure Pipelines is also engaged in the delivery of container images from the build agents to the Azure Container Registry while tracking digital signatures of the images and the original run of the pipeline.
Argo CD
By implementing GitOps, Argo CD changes the nature of the application deployment process for Kubernetes clusters. The application pipeline that was previously set up in Azure Pipelines no longer requires the use of the production Kubernetes API servers because the Argo CD agent running in the Kubernetes cluster is connected to Azure Repos and is able to monitor the used Git repository. When the pipeline modifies the files with the given declarative instructions, Argo CD identifies the mismatch between the actual cluster condition and the required state in Git and eliminates the discrepancies in the most secure way.
Flux
Flux is another example of a GitOps operator active in the cloud-native environment. It possesses a modular architecture design and an in-built integration with the control plane of Azure Kubernetes Service, introduced in Microsoft’s GitOps technology. In Azure DevOps environments, Flux checks the repository branches for the changes to the configurations and makes sure that Helm charts, policy constraints, and runtime manifests are deployed in the right cluster namespaces.
Secrets Management, Identity, and Governance
A major challenge faced by DevOps today is achieving a state of zero trust in continuous delivery pipelines while preventing them from becoming frail and insecure with constantly-changing API secrets.
Azure Key Vault and Workload Identity Federation
By 2026, the standard for securing CI/CD pipelines is to get rid of all static passwords for service principals completely. Workload Identity Federation is a way for Azure Pipelines to access Azure Key Vault using short-lived tokens issued by Microsoft Entra ID. Within jobs, it enables retrieval of database passwords and keys directly in RAM of deployed apps, without storing any credentials used in pipeline configuration. Access to Key Vault is tightly controlled via RBAC, so that only particular pipeline stages can access sensitive production secrets.
HashiCorp Vault
HashiCorp Vault serves as the single point of control for enterprise firms operating across several clouds and the hybrid operating environment. The HashiCorp Vault task integrates with Azure DevOps via short-lived pipeline credentials, thus allowing teams to obtain temporary credentials jointly for the infrastructure and application dependencies employed by the pipeline, whereas such credentials are discarded upon completion of the pipeline. Such a model of access allows minimizing the attack surface of the organization and altogether preventing credential duplication.
Azure Policy and Open Policy Agent
Governance as code guarantees following the rules of an organization from the viewpoint of compliance with corporate, regulatory, and architectural standards.
Azure Policy ensures that there are rules enforced directly at the level of Azure Resource Manager. The implementation of the Azure Policy occurs throughout the continuous delivery process during which all changes to infrastructure are approved according to the policies of the organization in question. It simply means that no changes can be made which would make storage accounts available to the public or disks unencrypted.
The Open Policy Agent (OPA): used with other tools like Conftest, Open Policy Agent enables programmers to develop general-purpose logic for compliance checks of Kubernetes and Terraform configurations and specifications within the pipeline without waiting for deployment instructions to reach the cloud system.
Observability, Monitoring, and FinOps
The process of deployment does not finish the job once the code reaches the environment of production. Nowadays, delivery models imply feedback loops that ensure monitoring of all important aspects of production like its stability, as well as performance and cost.
Azure Monitor and Application Insights
Azure Monitor and Application Insights serve as the main telemetry platform for applications using Microsoft technologies. Application Insights telemetry in Azure DevOps integrates with automated canary deployments and release gates. The pipelines will automatically check exception rates, server response times, and dependency failure rates after the release is rolled out. Whenever performance problems or high levels of defects occur, the system will halt all activities and trigger an automated rollback.
Prometheus and Grafana (Azure Managed Grafana)
Prometheus and Grafana are the leading industry-standard solutions for observability in cloud-native microservices and Kubernetes workloads. Prometheus supplies time-series metrics about both application endpoints and infrastructure nodes, while Azure Managed Grafana causes the metrics to form operational dashboards. The information from Grafana alerts with the help of webhooks is sent to Azure DevOps and triggers the creation of work items in Azure Boards or the execution of automation pipelines for the restoration of balance.
Infracost and Cost Management
Today’s software engineering practices are profoundly influenced by the combination of the FinOps approach into the CI processes. Infracost operates together with the pull request processes, enabling one to analyze the Terraform and Bicep definition and estimate the costs according to the already established cloud pricing schemes. When a developer proposes the infrastructural changes, for example, an increase of the computing pools or an increase of shelving capacity, Infracost puts the detailed estimation right into the comments of the pull request that prevents further surprises in terms of billing.
Artificial Intelligence and Its Impact on the Developer Productivity
Artificial intelligence in the world of 2026 has changed from theoretical brainstorming into the efficient automation of the processes which is reflected in high delivery speed and ease for developers.
Integration of GitHub Copilot Enterprise
GitHub Copilot Enterprise marks the use of artificial intelligence to develop enterprise-level software solutions. It leverages Copilot in Azure DevOps to help teams produce their YAML multi-stage pipeline files, to write pull-request messages, to provide unit test suites, and to spot potential logic errors before they become problematic. Using Copilot’s advanced architecture, it provides precise suggestions in the context of code used and architecture adopted. Thus, cognitive load is reduced, and companies can achieve fast delivery of their service.
Intelligent Application of Automated Pipeline Analytics
Modern Azure DevOps solutions employ machine learning algorithms that analyze pipeline data from different sources. They distinguish real errors occurring during compilation from temporary network failures and flaky tests. In addition, the state-of-the-art approach to intelligent automation can allow the automated retrying of transient errors and putting unclear integration tests into the quarantine process while issuing recommendations on overcoming frequent resource resolving problems.
The Blueprint of Strategy: Crafting an Internal Developer Platform
Above-mentioned tools provide enormous technical possibilities, but their full power is revealed when the tools are integrated into a purposeful and cohesive Internal Developer Platform (IDP). High-performing engineering companies do not make individual developers gather different tools for every project. Rather, platform engineers use Azure DevOps to serve as the orchestrator and create unified self-service golden paths.
In a mature environment of 2026, if an engineer needs to create a new microservice, he/she can use the self-service portal which triggers the automated pipeline for provisioning in Azure DevOps.
A repository of Azure Repos that comes with the organization's standard architectural templates, branching policies, and required pull request reviewers.
An Azure Boards backlog area corresponding to the delivery iterations and value stream tracking of the team.
Azure Pipelines pre-setup with a standard YAML template for integrating static security scanning, container vulnerabilities, and code quality checks.
An encrypted connection to an Azure Key Vault using federated identity eliminates the need for any manual credentials.
A declarative GitOps deployment manifest monitored by the in-cluster controller for an automated release to production.
Pre-configured observability dashboards in Azure Monitor or Grafana with predefined thresholds and canary-deployment rollback capabilities.
This integrated model decreases psychological burden, preserves high security and compliance levels in the organization, and helps developers concentrate on delivering business-critical logic.
With the advancement of technical innovations in the field of computation, developers and information specialists should be aware that it is not sufficient to know how to use any one tool at their disposal. Rather, they should be well-versed in assimilating the entire environment of tools available into a coherent continuous delivery process that is secure and resilient.
It involves consistent upgrading of skills to maneuver through this complex web of GitOps, secrets that operate under zero-trust principles, and automation powered by AI. Opting for a relevant devops azure course from OnlineITGuru prepares cloud engineers and platform professionals to back up their capabilities with skills that they can utilize while implementing and securing and executing delivery pipelines in 2026 and further.